ZeroNet RC MK IV
CODENAME: AIRPORT
Forensic Investigative Aggregation Platform — Encrypted Submission Intake, Analysis, and Case Management for Counter-Cyber-Intelligence Operations
(C) 2025-2026, BlackBox Computer Security Research & Development Team, Onetrak Digital Forensics L.L.C
Why ZeroNet RC4 Matters
For Cybersecurity
- Encrypted Intake — Submission data is processed by the receiving application and encrypted per-field with AES-256-GCM (ZNAES) before database storage.
- Defense in Depth — CSRF tokens, rate limiting, IP reputation filtering, optional API key authentication, and TLS certificate support provide multiple security layers.
- Forensic Analysis — Decrypt submissions in memory, search across decrypted text, and triage hosts by analytical flag categories (unique, high-volume, keyword-matched, mixed-indicator).
- Audit Trail — File-based rotating audit logs capture authentication events, configuration changes, and submission activity with 90-day retention.
For Law Enforcement & Investigations
- Case Graph Building (ATLAS) — Construct entity-relationship graphs from flagged hosts, linking infrastructure, identities, evidence, and threat intelligence into persistent case databases.
- Takedown Operations — Track and publish takedown actions against malicious infrastructure with partner attribution and verification timestamps.
- Public Threat Intelligence — Publish Most Wanted notices, public reports, and broadcast alerts through the web frontend for community awareness.
- Lab Script Generation — Export actionable bash scripts (Kali recon, evidence collection) against flagged hosts for field operations.
- Host Triage & Flagging — Automatically generate analytical flag groups to surface high-priority hosts, repeated abuse patterns, and evidence-bearing infrastructure.
- Partner Ecosystem — ZNRC4 operates within ODFSEC's wider network of technology and investigative partners, including cloud infrastructure from Akamai/Linode, encrypted services from Proton A.G., and collaborative frameworks with NCMEC and allied task forces.
Architecture
ZNRC4 is organized across three tiers — Web, Desktop, and CLI — all backed by an encrypted SQL Server database with ZNAES key storage. An offline recovery path (highlighted in red) accepts encrypted submissions via IIS CGI when the API server is unreachable.
flowchart TB
    subgraph Web["Web Tier"]
        direction LR
        API["API Server"]
        Templates["Page Templates"]
        Assets["Static Assets"]
        Recovery["Offline Recovery CGI"]
        EmergencyForm["Emergency Form"]
    end

    subgraph Desktop["Desktop Tier"]
        direction LR
        CT["Control Tower"]
        Atlas["ATLAS"]
        DV["DB Viewer"]
        LM["ListenMode GUI"]
        SC["Security Center"]
        PA["Public Admin"]
        AT["Admin Terminal"]
        FE["Flag Engine"]
    end

    CLI["CLI
Command Interface"]
    SQLDB["SQL Server
Encrypted database"]
    SOSDrive["SOS Drive"]
    ZNAES["ZNAES Keystore
AES-256-GCM tokens"]

    API --> SQLDB
    EmergencyForm --> Recovery --> SOSDrive

    Desktop -->|ODBC| SQLDB
    Desktop -->|Reads| ZNAES

    CLI --> Desktop
    CLI -.-> Web

    SOSDrive -.->|Manual Import| Desktop

    style Recovery fill:#1a0000,stroke:#ff0000,stroke-width:2
    style EmergencyForm fill:#1a0000,stroke:#ff0000,stroke-width:2
    style SOSDrive fill:#1a0000,stroke:#ff0000,stroke-width:2
Screenshots
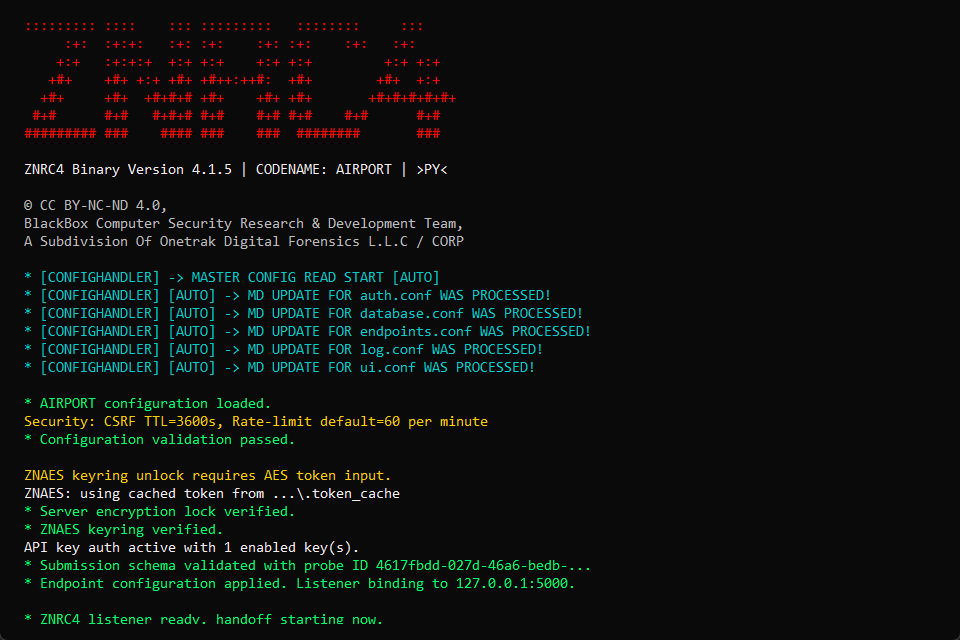
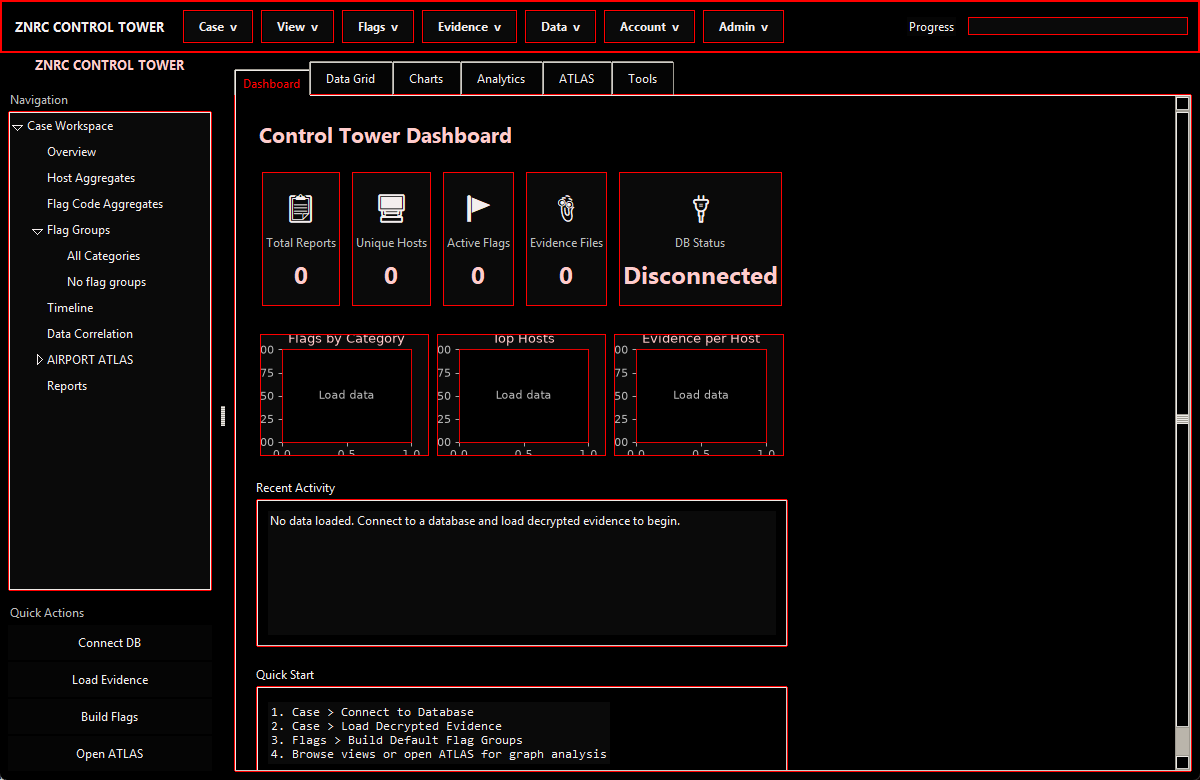
ZeroNet RC4 in action across its three tiers — CLI, Desktop GUI, and Web.
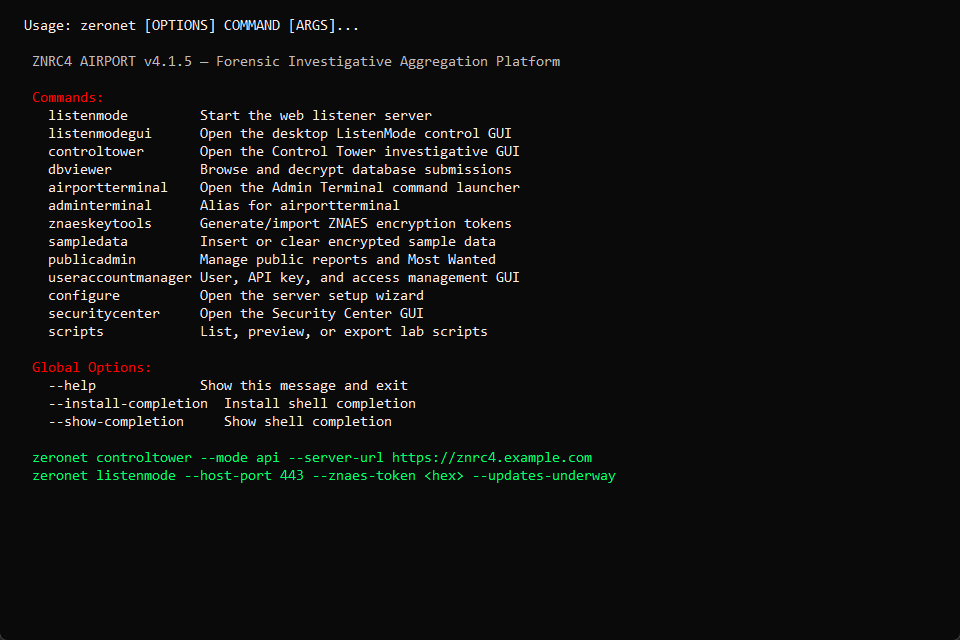
zeronet --help command tree listing all available subcommands and runtime options for both local and API modes.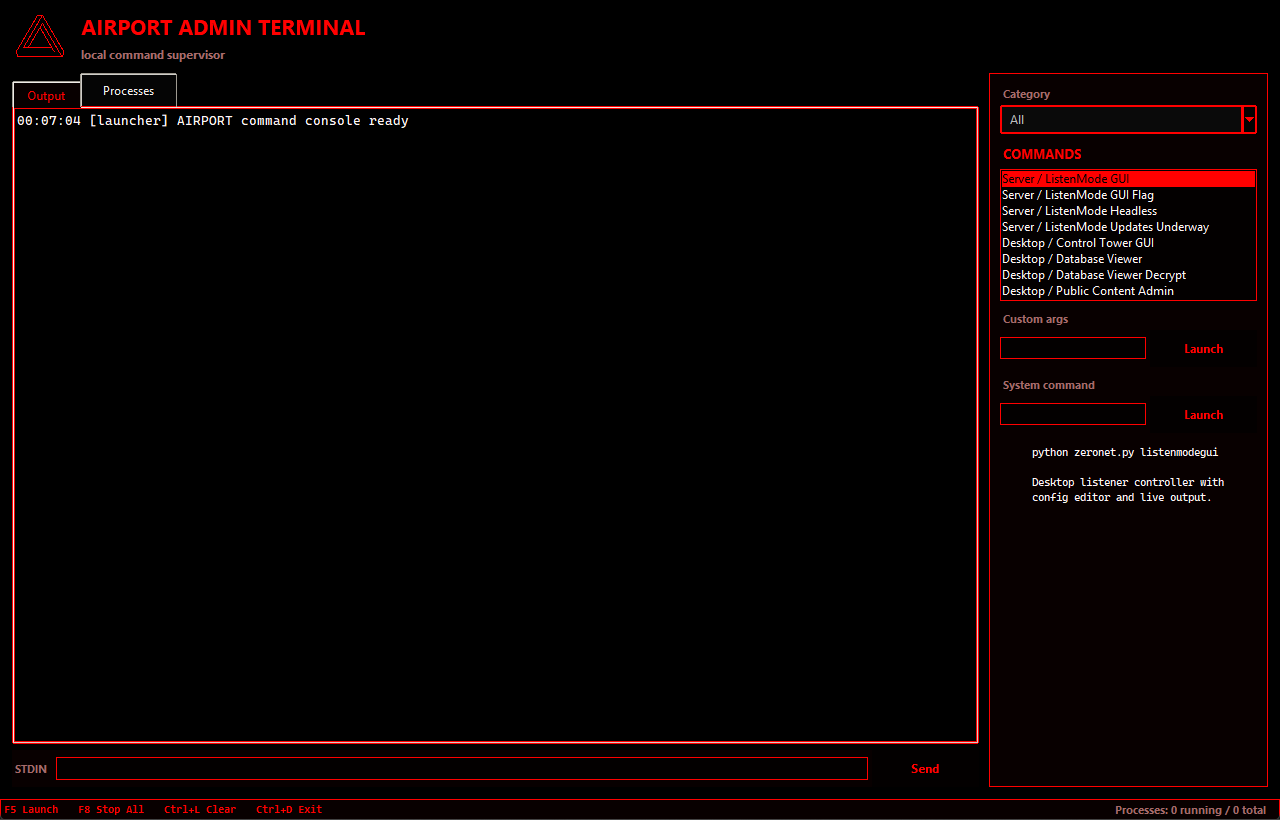
Platform Highlights
Separate web, desktop, and CLI interfaces let each team — from intake operators to analysts to administrators — work with the tool best suited to their role and security requirements.
Every submission field is individually encrypted before storage. Decryption happens only in memory on authorized analyst workstations — the server never has access to plaintext data.
CSRF tokens, rate limiting, IP allow/block lists, PBKDF2-HMAC-SHA256 API key authentication, and TLS 1.3 protect every layer of the intake pipeline.
Enterprise-grade Microsoft SQL Server backend with ODBC connectivity provides reliable, scalable storage for submissions, flags, cases, and audit records.
Build entity-relationship graphs linking hosts, infrastructure, identities, and evidence into persistent encrypted case databases. Export case visualizations for reporting and courtroom use.
Every authentication attempt, configuration change, and submission event is recorded in rotating audit logs with configurable retention. Enables compliance, accountability, and post-incident review without manual oversight.
Third parties submit abuse reports through a simple web form with file attachment support, automated tracking IDs, and real-time status lookup — no account creation or software installation required.
Desktop GUI tools for decryption, keyword search, host triage, and flagging — all running on the analyst's machine with decrypted data never written to disk.
Export actionable bash scripts for Kali-based field recon and evidence collection against flagged hosts. Generate downloadable evidence bundles for partner sharing.
Publish Most Wanted notices, takedown operation status, broadcast alerts, and downloadable intelligence reports through the public web frontend for community and partner awareness.